> For the complete documentation index, see [llms.txt](https://mamawhocode.gitbook.io/aws/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://mamawhocode.gitbook.io/aws/services/network/vpc.md).

# VPC

Virtual Private Cloud: your private cloud

[FAQs](https://aws.amazon.com/vpc/faqs/?saa=sec\&sec=prep) |

## Overview

* logically `isolated` virtual network.
* An AWS account comes with a `default` VPC network.

## Features

### VPC Peering

* a network connection between 2 VPCs.
* Non-onverlapping CIDR, non-transitive.
* 1 VPC can accept maximum 125 peering connection.

#### Benefits

* Support peering between multiple accounts.
* Inter-region: help connect cross-region.

<figure><img src="https://2259236002-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fuh9xZDZ53qGqmMCM44PU%2Fuploads%2Fgit-blob-b3e29a621c6b40ce11f79eac73931315dbee2942%2Ffigure_20230416150507.png?alt=media" alt=""><figcaption></figcaption></figure>

* do NOT support transitive communication
  * A peering B, B peering C -> A can not talk to C.
* It prevents:
  * Single Point of Failure.
  * Bandwidth bottleneck.

#### Establishing VPC peering

1. The **Requester** send peering request to **Accepter**.
2. The **Accepter** accepts peering request. If the peering is cross-account, both accounts must accept to activate it.
3. Manually add routes (IPv4 CIDR *of the peering VPC*) in each VPC.

<figure><img src="https://2259236002-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fuh9xZDZ53qGqmMCM44PU%2Fuploads%2FHTDI9UeEbl8GQKalwxnn%2Fimage.png?alt=media&amp;token=a7705e43-85f4-4667-a1ff-4165e961095a" alt="" width="563"><figcaption><p>Step to peering</p></figcaption></figure>

### Egress-only internet gateway (like a Nat gateway for IPv6)

* Allow output communication over <mark style="color:red;">**IPv6**</mark> from instances in VPC to the internet.
* Only use for IPv6, if you want to enable outbound-only internet over IPv4, use [NAT gateway](/aws/services/network/vpc/nat.md).

### AWS PrivateLink

* sharing services between different VPCs across AWS account
* does NOT need VPC peering, public Internet, NAT gateway, Route tables.
* help you `securely`, `privately` communicate with other AWS services.

### VPC Endpoint

<figure><img src="https://2259236002-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fuh9xZDZ53qGqmMCM44PU%2Fuploads%2FmSBAy5iFBA6EHFMv8Plt%2Fimage.png?alt=media&amp;token=0d6aee17-000e-43e5-b24e-144e24583bff" alt=""><figcaption><p>Privately connect to AWS service</p></figcaption></figure>

* Provide *<mark style="color:red;">private access</mark>* to AWS Services (S3, DynamoDB, CloudFormation, SSM) within VPC.
* VPC endpoint is a network gateway that allows communication between instances in a VPC and a service, such as Amazon S3, without requiring an Internet gateway or a NAT device.
* Data transfer between the VPC and the service through a gateway VPC endpoint is <mark style="background-color:yellow;">free of charge.</mark>
* There 2 types
  * ***VPC Interface endpoints***: <mark style="color:red;">**An ENI**</mark> with a private IP address that serves as an entry point for traffic destined to services powered by AWS PrivateLink.
    * Link to one or several subnets (for multi-AZ HA)
    * Link to a security group
    * Communicate with the service using an endpoint-specific private DNS hostname.
    * By default, the standard DNS names for SQS and SNS will use the public endpoint and not the interface endpoint. You need to use the private endpoint DNS.
  * ***VPC Gateway endpoints***: A gateway that is a target for a specified route in your route table. This type of endpoint is used for traffic destined to a supported AWS service, currently only <mark style="background-color:orange;">Amazon S3</mark> or <mark style="background-color:blue;">Amazon DynamoDB.</mark>
    * <mark style="background-color:blue;">Free of charge.</mark>

### Traffic Mirroring

Copy network traffic from <mark style="color:red;">ENIs</mark> for further analysis.

### VPC Flow logs

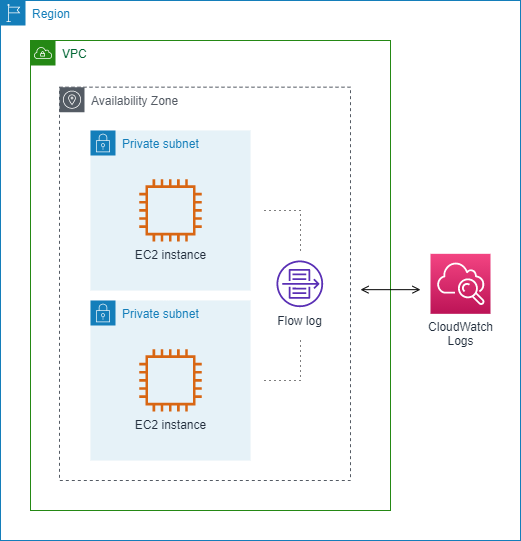
* Capture traffic going to & from ENIs.
* Export logs to CloudWatch or S3, or [Kinesis Data Firehose](https://docs.aws.amazon.com/vpc/latest/userguide/flow-logs-firehose.html)
* 3 types of flow logs: `Accept`, `Deny`, `All`
* Using **Athena** to analyze logs.

<figure><img src="https://docs.aws.amazon.com/images/vpc/latest/userguide/images/flow-logs-diagram-cw.png" alt=""><figcaption><p>eg: capture &#x26; publish flowlogs to CloudWatch</p></figcaption></figure>

{% hint style="danger" %}
After you create a flow log, you CANNOT change its configuration or the flow log record format. For example, you can't associate a different IAM role with the flow log, or add or remove fields in the flow log record. Instead, you can delete the flow log and create a new one with the required configuration.
{% endhint %}

#### Read flow logs

```
2 123456789010 eni-1235b8ca123456789 172.31.16.139 172.31.16.21 20641 22 6 20 4249 1418530010 1418530070 ACCEPT OK
```

<table><thead><tr><th width="70">#</th><th width="118">Field Name</th><th width="199">Example Value</th><th>Description</th></tr></thead><tbody><tr><td>1</td><td>version</td><td>2</td><td>The log stream version. If you see a value other than <code>2</code>, check the VPC Flow Logs documentation.</td></tr><tr><td>2</td><td>account-id</td><td>123456789010</td><td>The AWS account ID of the account that owns the source network interface for the flow log.</td></tr><tr><td>3</td><td>interface-id</td><td>eni-1235b8ca123456789</td><td>The ID of the network interface for which the log records.</td></tr><tr><td>4</td><td>srcaddr</td><td>172.31.16.139</td><td>The source IP address of the traffic.</td></tr><tr><td>5</td><td>dstaddr</td><td>172.31.16.21</td><td>The destination IP address of the traffic.</td></tr><tr><td>6</td><td>srcport</td><td>20641</td><td>The source port of the traffic.</td></tr><tr><td>7</td><td>dstport</td><td>22</td><td>The destination port of the traffic.</td></tr><tr><td>8</td><td>protocol</td><td>6</td><td>The IANA protocol number of the traffic. For example, TCP is 6 and UDP is 17.</td></tr><tr><td>9</td><td>packets</td><td>20</td><td>The number of packets transferred during the capture window.</td></tr><tr><td>10</td><td>bytes</td><td>4249</td><td>The number of bytes transferred during the capture window.</td></tr><tr><td>11</td><td>start</td><td>1418530010</td><td>The start time of the capture window in Unix seconds.</td></tr><tr><td>12</td><td>end</td><td>1418530070</td><td>The end time of the capture window in Unix seconds.</td></tr><tr><td>13</td><td>action</td><td>ACCEPT</td><td>The action that is applied to the traffic. Possible values are <code>ACCEPT</code>, <code>REJECT</code>.</td></tr><tr><td>14</td><td>log-status</td><td>OK</td><td>The status of the delivery of the log events to CloudWatch Logs. Possible values are <code>OK</code>, <code>NODATA</code>, and <code>SKIPDATA</code>.</td></tr></tbody></table>

## Security

## Cost

* Free
* But other feature such as NAT Gateway, VPC...will be charged.

## Best practice

## Trivia

* CIDR blocks of subnets can not be overlaped.
* The peering connection id has prefix **pcx**-
* `Default VPC` has Internet connectivity, so all EC2 instances inside it have public IPv4 addresses.
* 1 AWS account has up to 5 VPC / region. Need more? Go to `Service quota` to call AWS support.
* IPv4 is a ***default*** support, you can not turn it off. In other hand, IPv6 setting is optional, so you need to turn it ON if needed.
* The allowed block size in VPC is between a /16 netmask (65,536 IP addresses) and /28 netmask (16 IP addresses).
* VPC Flow Logs do not perform [***deep*** packet inspection](#concepts). They only provide metadata about the traffic such as the source, destination, and protocol.

## Concepts

* ***Deep Package Inspection*** (DPI): Traditional firewalls inspect basic data packet details such as sender, recipient, and data type, akin to checking a letter's address. Deep Packet Inspection (DPI), however, examines the packet's actual content, like opening the letter, enabling more precise control and filtering based on the contents, beyond merely the surface information.